SIDEC · 2026
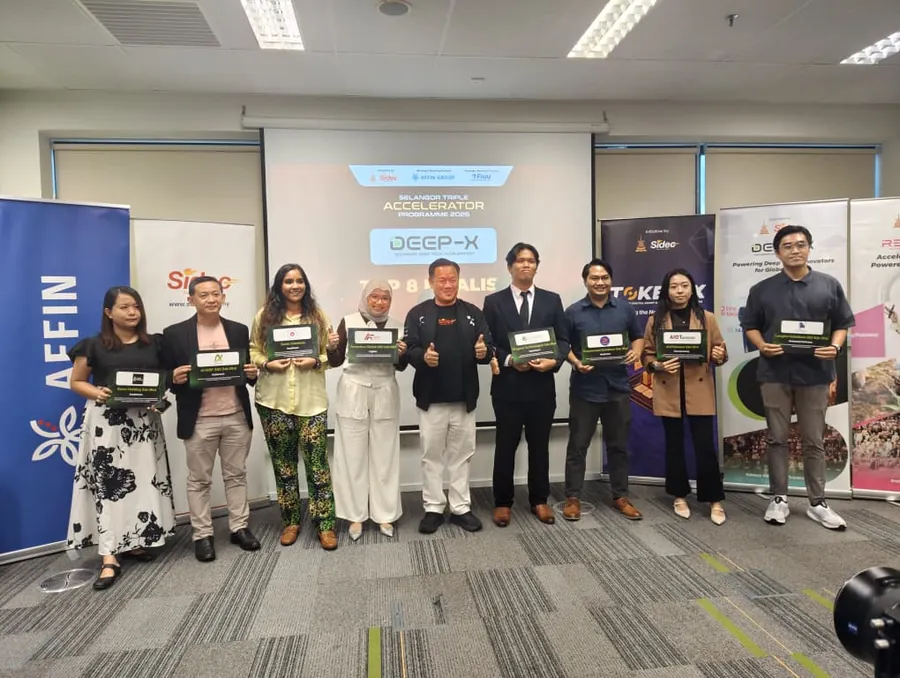
Deep-X Top 8 Finalist
Selected in the Cybertech category of the Selangor Deep Tech Xccelerator, supported by Affin Group and Fiuu.
Malaysia's sovereign AI cybersecurity platform
Fusion XDR unifies what happens inside your walls with what attackers see outside them — then correlates it into one risk-ranked attack story and contains it automatically or with your analysts.
Illustrative console
Recognition & events
Free · DigitalXposure by AI MSP 365
Get a free Exposure Snapshot of your external attack surface — read-only, no software to install, delivered within 24 hours under NDA.
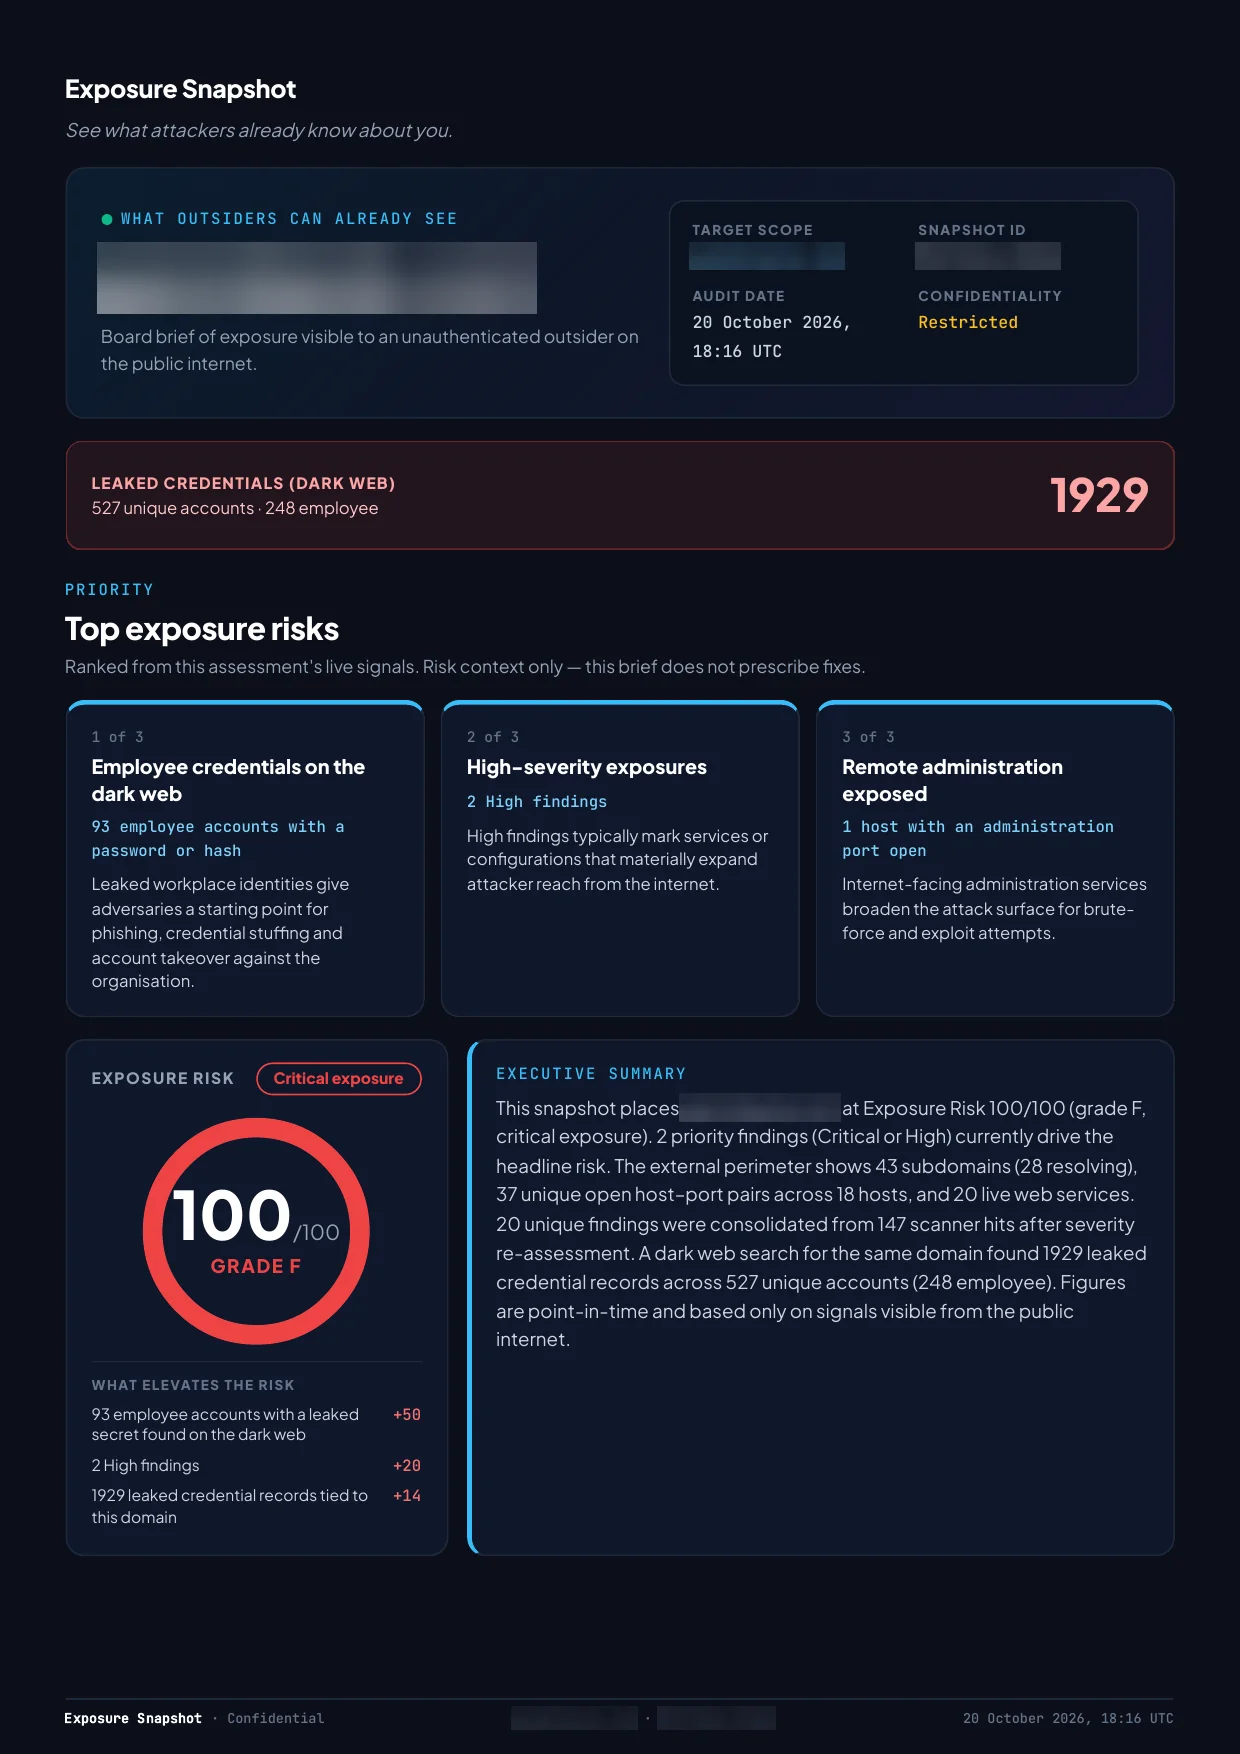

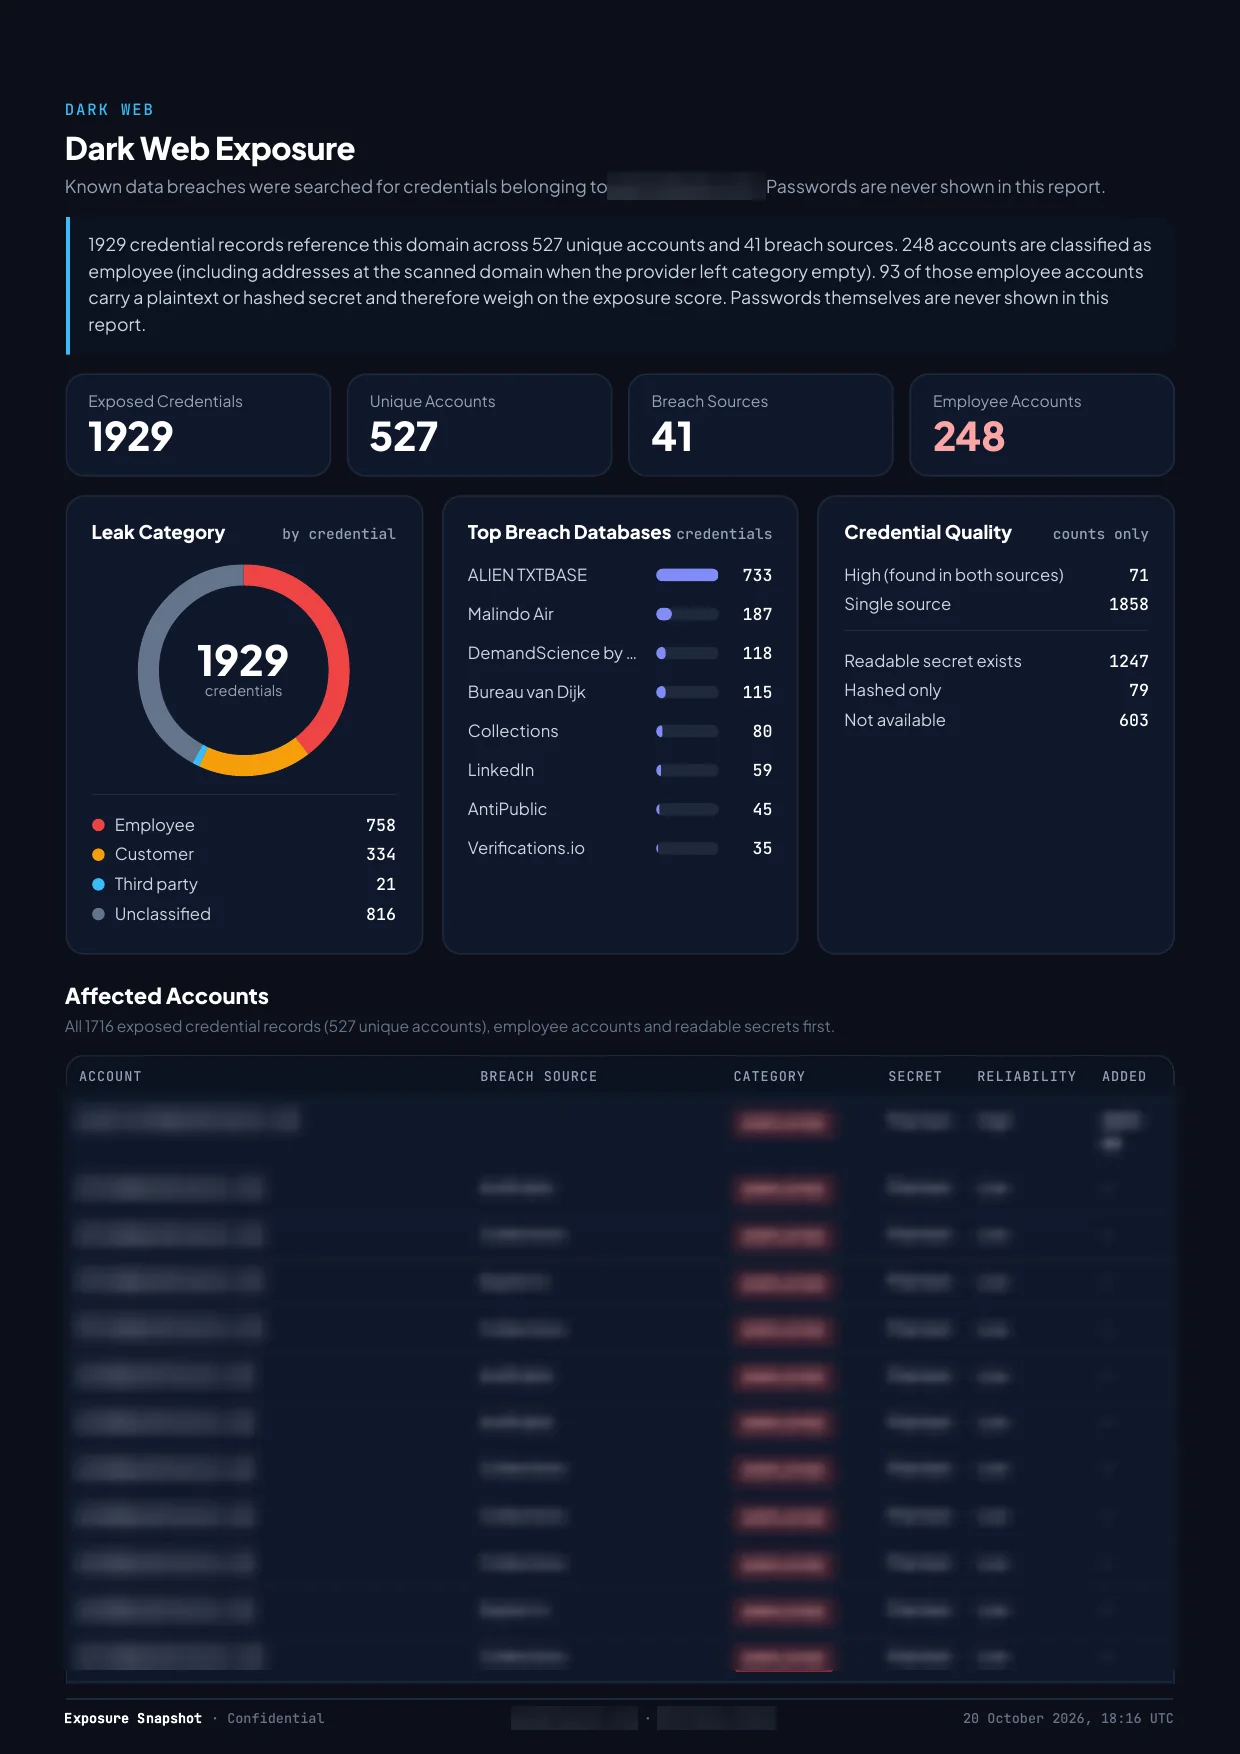
Real Exposure Snapshot, anonymised. Organisation, domains, accounts and IPs are redacted.
The problem
INSIDE YOUR WALLS
OUTSIDE YOUR WALLS
You can't connect the dots you can't see.
How Fusion XDR works
01 · UNIFY
Endpoint, server, network and web telemetry joined with dark-web, attack-surface and vulnerability intelligence.
02 · CORRELATE
Private AI connects evidence into a single case with MITRE ATT&CK context — not thousands of disconnected alerts.
03 · RESPOND
Playbooks block IPs, isolate hosts and quarantine threats, with full case management from triage to closure.
Live proof
SSH brute-force attack on a Linux server

The platform
01 · CORE
Centralised logging, correlation, threat hunting and incident response — the brain that turns every signal below into one attack story.
02
OS and database monitoring, log collection and security monitoring on Windows & Linux.
03
East-west traffic visibility, anomaly and lateral-movement detection across IT and OT/IoT networks.
04
Inline network protection: traffic filtering, access enforcement and perimeter visibility.
05
OWASP Top 10 protection, bot mitigation, and access & behaviour logging.
06
Continuous asset discovery, exposure monitoring and risk prioritisation.
07
Leaked-credential and data-leak detection with threat-intel alerts.
08
Continuous web and network scanning, prioritisation and reporting.
09
Host configuration checks, misconfiguration detection and hardening.
Why sovereign AI
Your data goes to the internet
Your data stays with you
Beyond the platform
Human risk · with our APAC partner COMING SOON
Technology stops attacks — people start most of them. We measure human risk, run evidence-based behaviour-change programmes, and verify real adoption with Fusion XDR telemetry.
TVET · Universities · Corporate upskilling
Hands-on SOC training on the same platform that defends Malaysian organisations. Learners attack, detect and respond in real labs — from any browser.
Deploy your way
FOR AGENCIES & CNII OPERATORS
The full platform and private AI inside your environment, including air-gapped networks. Your team operates it with our engineering support.
FOR ENTERPRISES & SMEs
Our Malaysia-based analysts monitor, hunt and respond around the clock — no SIEM or SOC build-out needed.
Solutions by sector
Compliance
Fusion XDR maps controls and evidence to the frameworks Malaysian regulators and auditors expect.
Case study · 2023 · Regulated organisation in Malaysia (anonymised)
Why? No single tool saw the full attack.
Reference case · Regulated body (anonymised)
None of them appeared in the annual penetration test report — it was never designed to look.
Why dark-web monitoring matters →What changes with Fusion XDR
Case studies are anonymised to protect confidentiality. Identifying details such as names, dates and sectors are withheld or generalised, figures are rounded, and the accounts are shared for awareness only — they do not describe the current security of any organisation.
Built by practitioners
Well-equipped organisations still lose when their tools don't talk to each other. Fusion XDR is designed by security architects to close exactly that gap — every signal, one attack story.
About AI MSP 365 →Leadership
Kevin Lim, CISSP
Founder
Cybersecurity leader with a proven track record across industries, leading the team that builds Fusion XDR.
SIDEC Deep-X Top 8 Finalist 2026 · MDEC MADI Top Winner 2025
Recognition & events
SIDEC · 2026
Selected in the Cybertech category of the Selangor Deep Tech Xccelerator, supported by Affin Group and Fiuu.
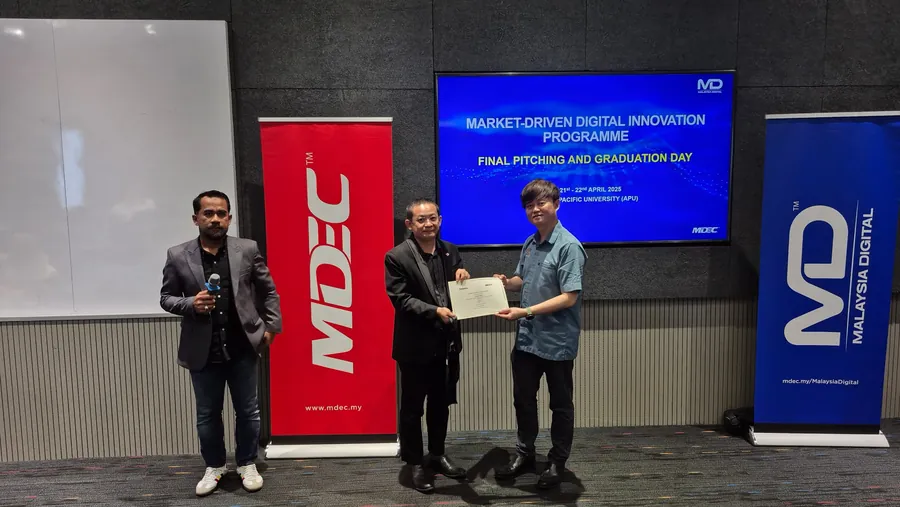
MDEC × DELOITTE · 2025
Market-Driven Digital Innovation Programme, final pitching and graduation day.
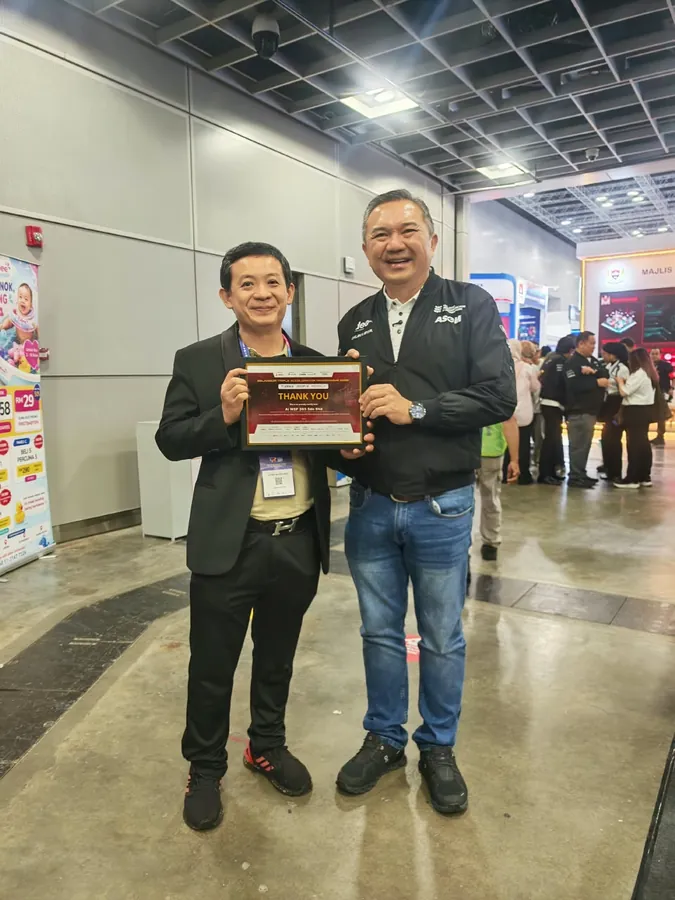
SELANGOR · 2026
Appreciation for AI MSP 365's participation in the Selangor Triple Accelerator Programme 2026.
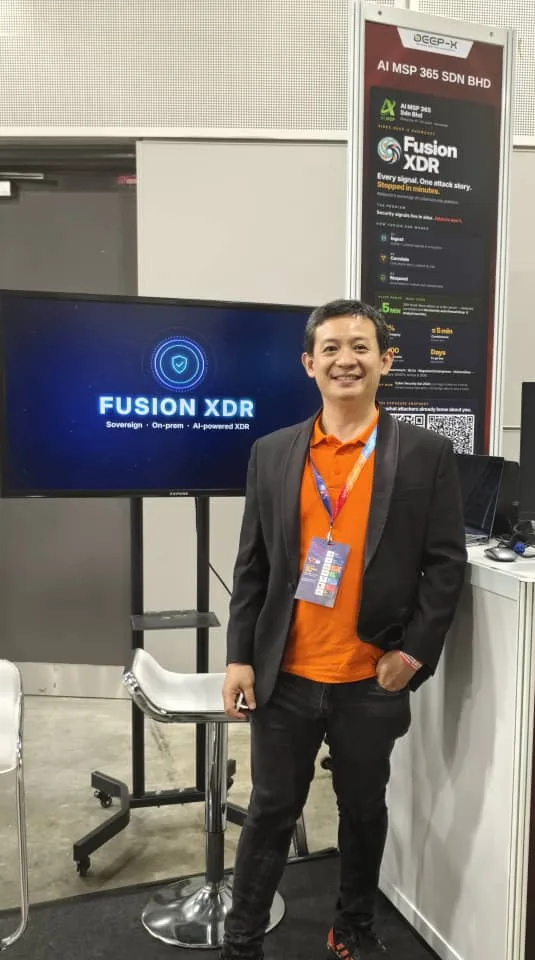
AiSEM · 2026
Fusion XDR showcased on Startup Street with the SIDEC startup pavilion, October 2026.
From the blog
DARK-WEB MONITORING
A regulated body found more than 1,000 of its 40,000 member accounts on the dark web. None appeared in its pen test report. Here's why — and what to do about it.
EXPOSURE MANAGEMENT
43 subdomains, 37 open host-port pairs and an exposed admin port — from one external scan. Why your attack surface is bigger than you think, and how to manage it.
SECURITY MONITORING
Best-in-class tools, annual pen tests and a DR centre didn't stop a destructive ransomware attack. Here's what was missing — and what a SOC actually does.
FAQ
Fusion XDR is a sovereign AI cybersecurity platform developed in Malaysia by AI MSP 365. It combines XDR and SIEM with network traffic analysis, a web application firewall, inline network protection, exposure management, dark-web credential monitoring, automated vulnerability assessment and host configuration checks — correlated into one attack story in a single console.
Yes. Fusion XDR and its private AI can be deployed entirely inside your environment, including air-gapped networks, so telemetry and evidence never leave your jurisdiction. It is also available as a managed service run by our Malaysia-based SOC.
Fusion XDR provides continuous monitoring, incident detection and response, case management and audit-ready evidence that NCII entities and their service providers need to demonstrate under Act 854 and the related NACSA codes of practice.
It is a read-only external assessment, delivered by DigitalXposure, that shows what attackers can already see about your organisation: leaked credentials on the dark web, exposed systems, forgotten assets and a board-ready risk score. Nothing is installed and results are delivered under NDA, usually within 24 hours.
Yes. Managed Fusion XDR is a 24/7 SOC-as-a-Service operated by our analysts in Malaysia, including monitoring, threat hunting, incident response and monthly executive and compliance reporting.
Yes. Ransomware recovery is one of our professional services, alongside compromise assessment and audit & compliance reviews. Contact us on WhatsApp at +60 13-538 7268 for urgent incidents.
Book a 30-minute demo with a Fusion XDR specialist. We'll walk through your threat landscape and show how the platform fits — on-premise or managed.